Risk Advisory

People Helping People

Banner

ㅤ

ㅤ

Risk Advisory Services


Markets and businesses operate in increasingly complex and fast-changing environments. New and evolving risks threaten companies’ ability to achieve their strategic objectives. At the same time, stakeholders are demanding more information, greater transparency and sound corporate governance. Against this backdrop, expert support for comprehensive enterprise risk management is becoming increasingly necessary to protect and enhance brand value and business efficiency.

We must also bear in mind that increasingly sophisticated technology environments, a heightened risk of fraud, regulatory pressure and the need to cut costs and streamline control activities make it essential to have true specialists to manage and control a company’s key risks.

To this end, BDO’s Risk Advisory division offers services in internal audit, risk management and control, regulatory compliance and good governance, aimed at:

¿Why choose BDO?

  • Providing assurance over your risks and reducing them.
  • Establishing efficient and effective controls at an appropriate cost.
  • Supporting your internal audit function.
  • Ensuring regulatory compliance and good corporate governance.
  • Improving process efficiency and control.

¿How can help you?

Internal Audit


Internal audit has evolved. It is no longer simply a means of assessing quality, but a strategy for creating value across the whole organisation. Internal audit plays a crucial role in providing assurance over and controlling the risks that may affect the achievement of companies’ strategic objectives.
 

BDO’s internal audit specialists bring innovative approaches to help companies assess the effectiveness of their operational functions and processes. They also work alongside Internal Audit and Internal Control departments on assignments in areas that require greater specialisation or where additional specialist resources are needed.

  • Internal audit outsourcing and co-sourcing.
  • Outsourcing of the internal audit function in regulated entities subject to CNMV (Spanish National Securities Market Commission) or Bank of Spain requirements.
  • Internal review of anti-money laundering (AML) / sustainability compliance.
  • Quality assessment reviews (QAR) / assessment of alignment with the Institute of Internal Auditors’ Global Internal Audit Standards.
  • Support to the Audit Committee.
  • Support in preparing risk maps for internal audit.
  • Analysis, development and implementation of internal audit tools.
  • Implementation of continuous auditing systems: remote auditing of key risks.

Internal control 
and risk management


In a business environment marked by uncertainty and complexity, sound management of the risks organisations face has become a cornerstone of their growth and long-term viability. Identifying, assessing and anticipating risks enables companies not only to protect their assets and reputation, but also to ensure business continuity in the face of potential threats.

Internal control systems play an essential role in this process, as they provide a structured framework for preventing and mitigating risks. Through specific policies, procedures and controls, internal control systems help ensure the effectiveness of the preventive measures in place and the reliability of the information reported to the market and stakeholders. They also enable potential deviations or incidents to be detected early, allowing for a swift and effective response that minimises the negative impact on the organisation.

Integrating risk management and internal control systems into corporate governance models fosters a culture of continuous improvement and prevention, which is essential in today’s environment. When both elements work together, organisations not only strengthen their response mechanisms and resilience to risk factors, but are also better placed to seize opportunities and successfully tackle the challenges of a competitive landscape.

  • Design and implementation of enterprise risk management (ERM) systems.
  • Risk analysis and assessment. Design and development of risk maps.
  • Design, implementation or assessment of internal control systems (ICFR, ICSR, SOX, etc.).
  • ISAE 3402, SSAE 18 and ISAE 3000 reviews. Visit site
  • Supplier and outsourced service control systems (vendor risk management). Visit site
  • Setting up or improving process control systems.
  • Development, control and updating of processes and procedures (internal regulations).
  • Prevention and control of internal and external fraud.


Cumplimiento Normativo


In recent years, the volume of regulation affecting organisations has grown steadily, at both national and European level. Market globalisation, digitalisation and growing concern over issues such as sustainability, data protection and transparency have driven the emergence of new regulations and frameworks.

This regulatory growth requires companies to remain constantly vigilant in order to identify and understand the obligations that apply to them, thereby avoiding penalties and reputational damage that could compromise their business and brand value.

Against this backdrop, organisations need to develop compliance management models tailored to the complexity and fast-changing nature of the regulatory landscape, integrating policies, procedures and tools that support the implementation, monitoring and updating of their compliance systems. Only through proactive management aligned with international best practice can they adapt and respond to regulatory change while remaining competitive.

BDO has experts in regulatory risk management and compliance who work with companies to implement, adapt and assess their compliance models.

  • Criminal compliance: design of criminal, tax and other compliance models aligned with best practice, alignment of models with reference frameworks (UNE 19601, UNE 19602, ISO 37001, ISO 37301) and development or updating of model components (code of ethics, operating manuals, compliance policies, etc.).
  • Compliance model audits and pre-certification audits in accordance with the above standards.
  • Compliance risk assessment: assessment of exposure to regulatory risks and of the control frameworks in place to mitigate them.
  • Anti-money laundering: analysis of suspicious activity, transaction review and approval, development of procedure manuals, external expert review, etc. Visit site
  • Implementation of compliance systems and tools.
  • Internal reporting system (whistleblowing channel): implementation and outsourced management. Visit site
  • Privacy: audits, DPO support, etc. Visit site
  • Audit, advisory and compliance services relating to sustainability regulations. Visit site
  • Standards of conduct: articles of association, board and general meeting regulations, board committees, internal code of conduct, conflict of interest policy, business ethics and corporate governance.
  • Solvency II compliance services for the insurance sector. Financial and actuarial analysis. Solvency and Financial Condition Reports (SFCR). IFRS 17. Insurance distribution regulation. Visit site
  • MiFID compliance and compliance monitoring services for the financial sector.

Corporate Governance and ESG 


In today’s context, organisations face an environment marked by high uncertainty, stemming from factors such as rapid technological change, geopolitical volatility, environmental challenges, high-impact regulatory changes, growing competition and shifting market trends driven by globalisation.


Adapting to this changing environment requires organisations to move towards proactive management models that embed sustainability and risk management at every level. This means strengthening a culture of compliance and business ethics, fostering transparency, promoting internal control frameworks and establishing mechanisms for dialogue and collaboration with stakeholders.

As a result, corporate governance takes on strategic importance, as it provides the framework needed to anticipate, identify and manage the potential risks the organisation faces.

To meet the expectations of the market and stakeholders, BDO’s teams work with companies’ management and boards of directors to strengthen their control and governance frameworks.

  • ESG services. Visit site
  • Risk management and internal control model services. Visit site
  • Analysis, assessment and improvement of governance systems.
  • Design of stakeholder communication and reporting models.
  • Development and implementation of codes of conduct.
  • Design or assessment of compliance models.
  • Setting up and managing whistleblowing channels. Visit site
  • Development of governance models for non-financial reporting and transparency: materiality assessment, KPIs, policies and procedures.

IT audit, security 
and technology risk management 


We assess technology, information security and cybersecurity risks and carry out IT audits to mitigate risk, minimise threats and comply with regulations and other requirements relating to information systems. Our specialists have extensive knowledge and experience aligned with the most widely recognised certifications in information security.

  • IT audits and audits of outsourced IT processes.
  • IT compliance audits (DORA, NIS2, EIOPA guidelines, SWIFT, TARGET2, Iberpay, TRA audit, RED Directive).
  • Privacy and data protection (GDPR, LOPDGDD).
  • Business continuity and IT service continuity.
  • Cybersecurity (penetration testing, application security, web environment security, Wi-Fi security, security office).
  • AI and privacy (AI governance, EU AI Act, AI risk assessment, ISO 42001 good practice).
  • National Security Framework (ENS) certification (Royal Decree 311/2022). Visit site
  • PINAKES qualification service.
  • Technology risk management: IT vendor risk management.
  • Gap analysis against cybersecurity policies, standards and procedures.
  • Critical infrastructure.
  • Cloud computing: cloud assessments and services.
  • DevOps / demand management / change management.
  • Endpoint security.
  • Data governance.
  • Data mining and data analysis.
  • Gambling sector regulation. Visit site

Other Risk Advisory services


Our Risk Advisory services in internal audit, risk management and control, regulatory compliance and good governance include, among others, the following specialist services:

Risk is everywhere: responsibility for managing it extends across the whole organisation, beyond the risk function


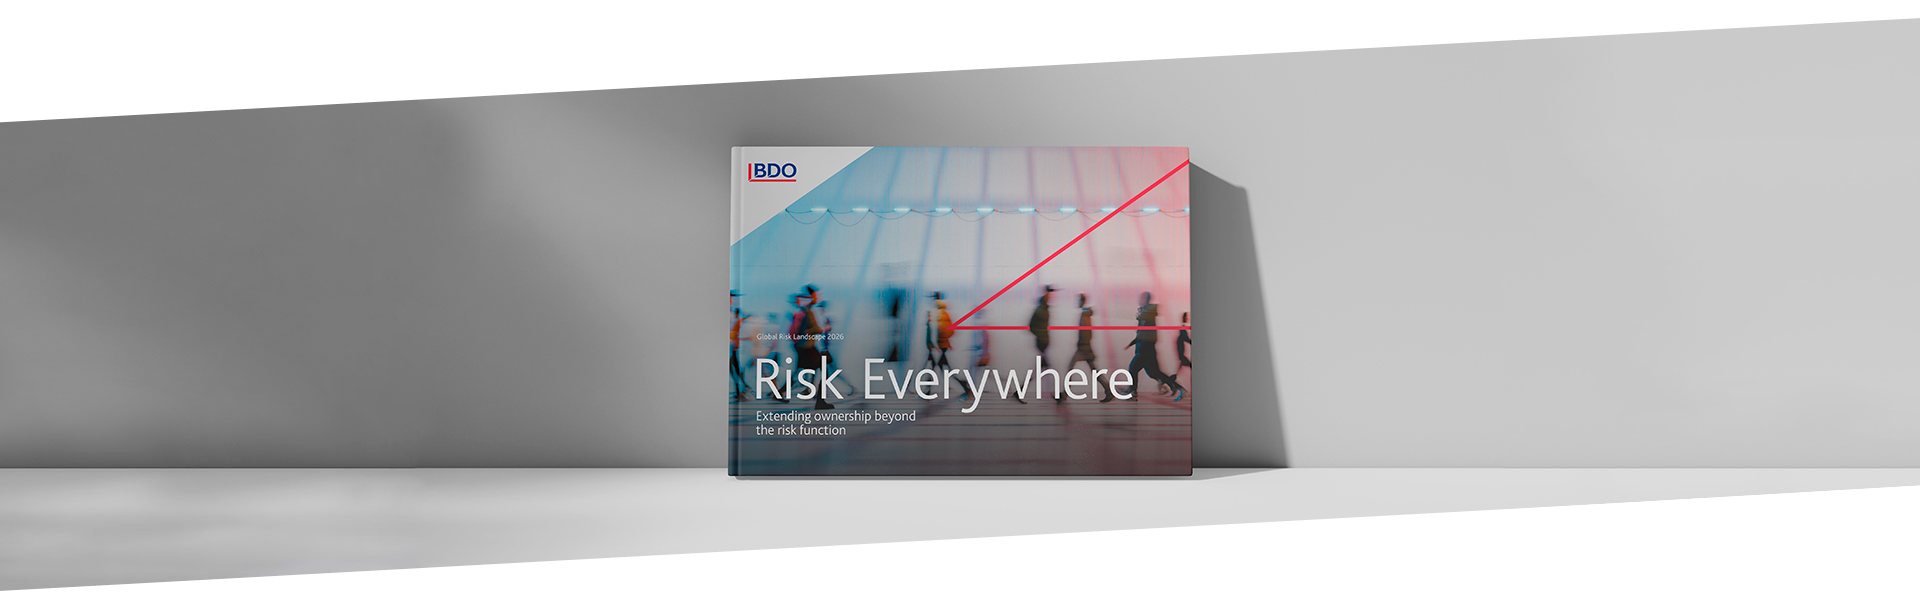
The global risk landscape has changed dramatically. What were once isolated risks are now deeply interconnected, fast-evolving threats, amplified by geopolitical instability, technological disruption and economic volatility. For business leaders, change and disruption are no longer the exception: they have become the norm.

The Global Risk Landscape 2026 report examines how organisations can respond to this new reality by rethinking the way risk is understood, taken on and managed. Drawing on the views of 500 executives across key global markets, the report reveals the risks to which organisations are most exposed and the challenges that arise from taking a traditional approach to risk management.

Notas sobre el original:


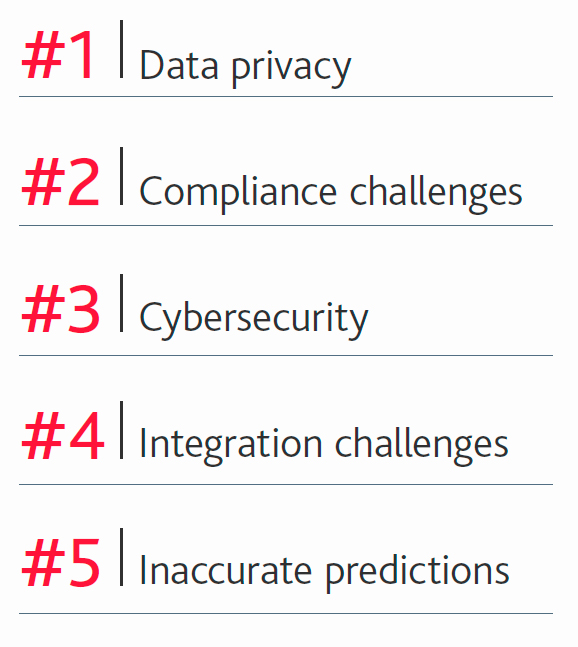
The main AI risks lie in data, regulatory compliance and integration

The top five AI risks that concern business leaders most.


Companies face increasingly complex environments, with changing risks and growing demands for transparency and good governance. In this context, having specialists who can help manage risk and protect business value is essential. At BDO, we support our clients in internal audit, risk management and control, and regulatory compliance, with a clear goal: to reduce risk, ensure sound corporate governance and improve the efficiency of their processes.”

Gonzalo García-Liñán

Gonzalo García-Liñán

Risk advisory services Partner
View bio